Memory: what RuVector secures, and where sgit addsRuVector README · Security and governance
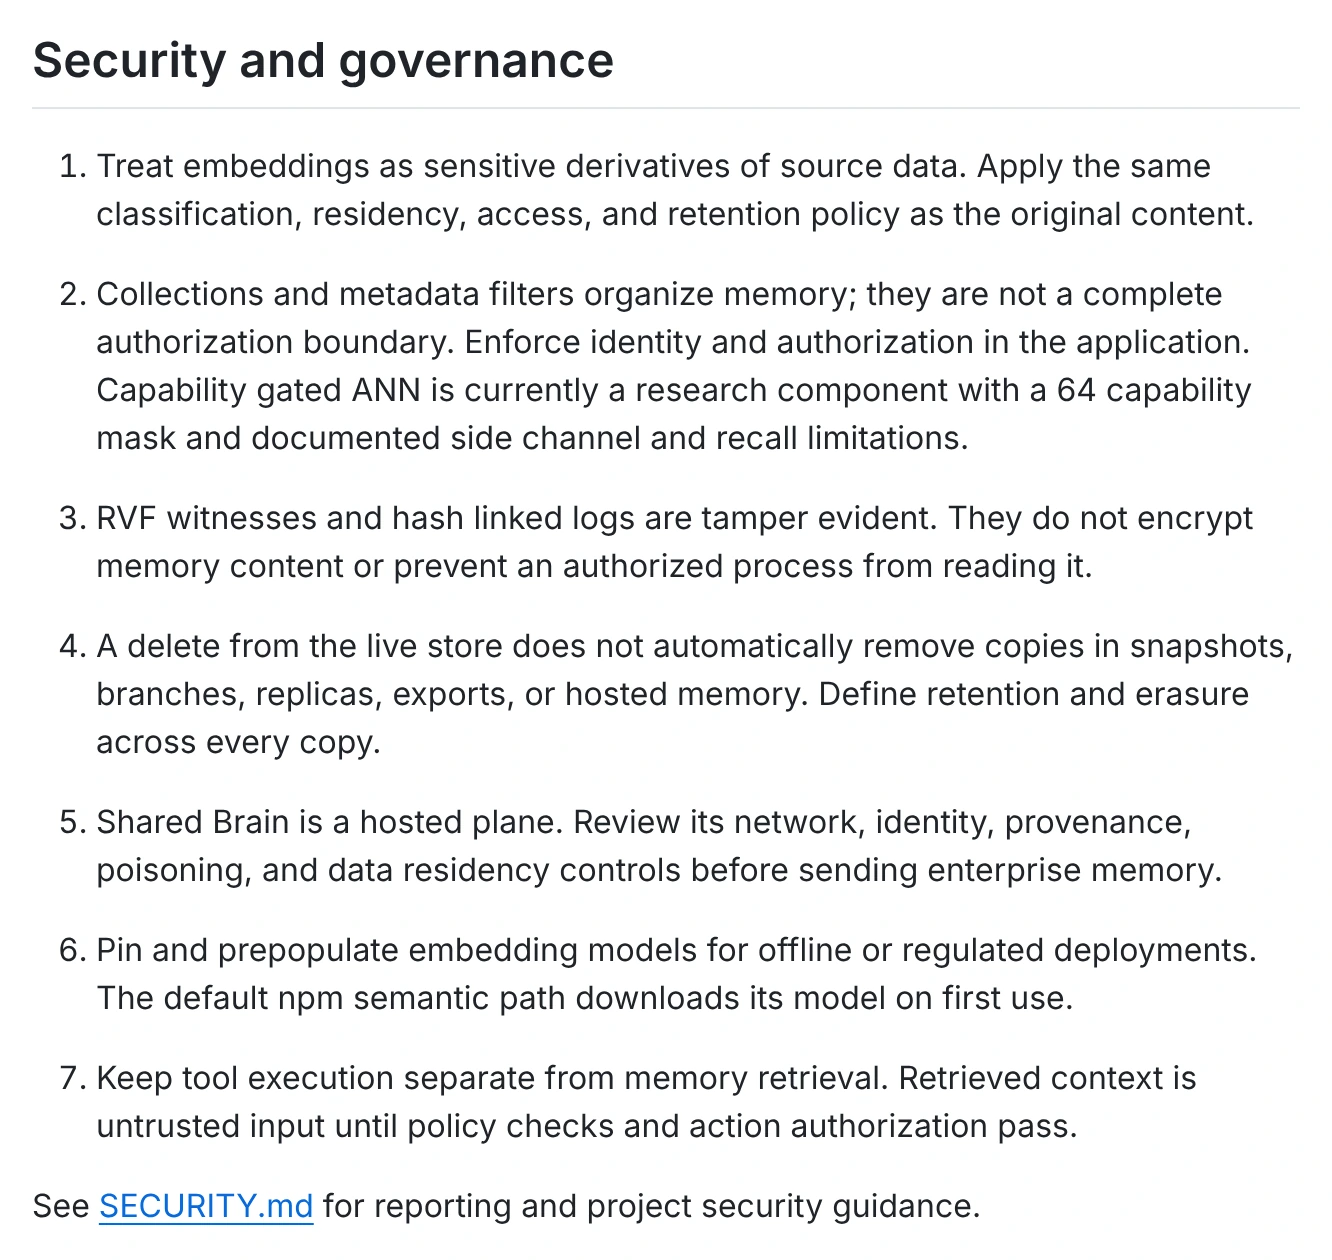
README.md · github.com/ruvnet/ruvector
Security and governance · read 15 Oct 2026
Security and governance · read 15 Oct 2026
What RuVector securesin its own README, credited first
Where sgit addsaround the files: an encrypted vault
Security and governance, 3
“RVF witnesses and hash linked logs are tamper evident.”
README: “They do not encrypt memory content …”
+ Content encrypted on the client, AES-256-GCM: the server stores ciphertext only
Library and capability map
“Full snapshots” and “Copy on write branches”: “Isolated memory experiments without full copies”
beside its snapshots and branches
+ A history shared across machines: pushed, merged, cloned
Security and governance, 4
“Define retention and erasure across every copy.”
README: “A delete from the live store does not automatically remove copies …”
+ One vault per run, deleted with the run, and the delete checked
RuVector is the memory substrate; sgit wraps the files. rUv + sgit.
Screenshot of README.md on main, 15 Oct 2026; quotes exact. RuVector: MIT, by rUv / ruvnet. sgit figures: data/vaults.json. agent@riskmandate.ai